PHP 8.2 Is Now Stable and Available on SiteGround Servers

stable release of php 8.2 version

PHP 8.4: Stay Updated! 🚀 Check out our latest blog post to explore the newest features and enhancements in PHP 8.4.

It’s that time again! Time for the Santa ElePHPant to visit all the good little PHP developers around the world and shower them with new goodies that make it easier for them to build the web.

As of this writing, PHP 8.2 is in Release Candidate 1 (RC1) status. We are in the late stages of development and bug fixing for this version and you can tell because forward looking web hosts like SiteGround are now making the RC builds available for their clients to test with. (Did you see the word TEST there? For those who don’t know what that means, it means NOT IN PRODUCTION!)

So let’s take a look at some of the new presents that Santa ElePHPant is bringing us.

New Goodies

First up, let’s take a look at a few of the new features that will be of interest to PHP developers. This is not an exhaustive list of the new goodies in Santa ElePHPant’s bag. It’s more a short list of the things I think the majority of PHP developers will be interested in.

readonly classes

In PHP 8.1 we got readonly properties for classes. This was a great leap forward for a lot of projects. However, there is still a small hole that needed to be plugged, clases. Yes, you can make every typed property in a class as read only and you are good to go, but honestly, that’s a lot of typing and if we know anything, we know that developers are lazy. So instead, in PHP 8.2 we can mark an entire class as readonly.

readonly class MyClass {
    public int $myProp;
    public string $myOtherProp;
    public __construct(string $myOtherProp, int $myProp) 
    {
        $this->myProp = $myProp;
        $this->myOtherProp = $myOtherProp;
    }
}

Here we have a class defined as readonly. We have 2 properties of the class and both of them are inherently readonly. The readonly rules from PHP 8.1 still apply. You can initialize the property only once, after that it is set. 

$myObj = new MyClass(‘Cal was here’,42);

However, once they are initialized, they are now immutable.

$myObj->myProp = ‘Cal is no longer here’;

// Fatal Error: Uncaught Error: Cannot modify readonly property MyClass::myProp

One other behavior of the readonly class is that properties cannot be dynamically added to the class, ever. Below we talk about deprecating Dynamic properties and how that’s a good thing. There is even an annotation that allows you to override this. However, if you mark a class as readonly, then it cannot be overridden.

Constants in Traits

Traits have been with us in PHP since PHP 5.4. They have long been the language’s answer to “composition over inheritance”. Now traits are getting an interesting new feature, the ability to define constants in a trait.

trait MyTrait {

    private const MY_CONSTANT = 42;

}

Now, if your trait uses a constant, you can define it in the trait and not have to remember to define it in each class that uses the trait.

trait MyTrait {

    private const MY_CONSTANT = 42;

    public function meaningOfLife() : int

    {

        return self::MY_CONSTANT;

    }

}

class MyClass {

    use MyTrait;

}

$myObj = new MyClass();

echo $myObj->meaningOfLife(); // prints 42

Like everything in life, there are a few rules.

Traits can define class constants. If a class uses that trait it can also define the same class constant as long as both the visibility and value are exactly the same. So the example above works but the one below will trigger a fatal error

trait MyTrait {

    private const MY_CONSTANT = 42;

    public function meaningOfLife() : int

    {

        return self::MY_CONSTANT;

    }

}

class MyClass {

    use MyTrait;

    public const MY_CONSTANT = 42;

}

Still, even with the rules that you have to follow, this is a real step forward. Traits are a great way to share code between classes and now they are even more self-contained.

Random Extension 5.x + Random Extension Improvement

The original PHP random number generator is still in the base code. It’s never been great and it’s absolutely useless for cryptographic uses. In PHP 7, we got a couple new functions, random_int() and random_bytes(). They went a long way to fix the problems but under the hood, they are just interfaces to the native OS’s random number generator. At the time this was a good solution but the problem is it’s a slow one. 

Now with PHP 8.2 we get not only an entirely new Random number generator, it is built into PHP,  and we get an extensible object oriented interface to it.

This is actually two different RFCs that I’m lumping together. After the first one “Random Extension 5.x” was voted on and passed, it was discovered that there was a few issues with it. A second RFC, “Random Extension Improvement”,  was prepared and voted on to fix the issues found with the first one.

The end result is a new set of classes that give us better pseudo-random numbers in PHP.

While we are actually getting several new random number generators (RNG), for simplicity I’ll discuss the new Random\Engine\Secure class.

$engine = new Random\Engine\Secure();

$randomString = $engine->generate(); // a random binary string

echo bin2hex($randomString); 

Now if we want to do something like sort an array, we need one of the new Randomizer objects. 

$randomizer = new Random\Randomizer($engine);

$items = range(1, 10);

$randomizedItems = $randomizer->shuffleArray($items);

print_r($randomizedItems);

Now in the above example, we used the Secure engine. The secure engine does not accept a seed and will always generate a non-reproducible string. The engines that allow you to specify a seed will produce the same results each time if you use the same seed. 

The Randomizer class also provides several other methods that are really what PHP developers are looking for.

  • getInt() : int
    This replaces the old mt_rand() function
  • getInt(int $min, int $max) : int
    This replaces both the old mt_rand() function as well as the newer random_int() function.
  • getBytes(int length): string
    This replaces the random_bytes() function 
  • shuffleArray(array $array): array
    This replaces the old shuffle_array() function
  • shuffleString(string $string): string
    This replaces the old str_shuffle() function

Among other things, since this brings all of the randomizing functionality into a single area of the engine, it streamlines the core code and will make further improvements easier.

“So long and thanks for all the fish”

All good things must come to an end and that includes some features and commands of PHP. Let’s look at a couple of the important deprecations that if you aren’t careful will end up causing you problems.

Deprecate dynamic properties

At first blush, this one seems like it’s going to be a huge problem. Since PHP got the current object model, it’s been possible to add properties to an object any time you want. Now somebody thinks this behavior is a bad thing. (HINT: It was always a bad thing but one a lot of developers took advantage of.)

class MyClass {

    public string $name;

}

$myObj = new MyClass():

$myObj->nmae = ‘Cal Evans’;

Notice that I misspelled the property name. I know I’m probably the only developer who has misspelled a property name but in PHP when it happens, I get a new property on the object and the original property remains unchanged. That was not my intent.

Starting with PHP 8.2, this will emit a DEPRECATED WARNING.

There are 3 exceptions to this new rule.

  1. Any instance of StdClass will still be able to accept dynamic properties.
  2. Any class with magic __get() and __set() methods will still accept any property.
  3. Any class that has the compiler annotation #[AllowDynamicProperties] and any child class will allow dynamic properties to be set.

So while all is not lost for those that depend on this “feature” of PHP, if you are still going to use it, you are going to have to make some changes to your code. 

The good news is that all that will happen right now is the warning emitted to the log files. So while it might fill up your log files reminding you that you need to fix this, PHP 8.2 won’t break your code. That happens in PHP 9.0 when the warning – and the ability to automatically add dynamic properties – gets removed from PHP.

(Partial) Deprecate ${} string interpolation

This is another depreciation that on the surface I thought was going to be a huge deal. Turns out, it is probably not going to affect many developers.

There are 4 ways to implement the “{$variableName}” syntax, 2 that make sense, and two that don’t. The two that don’t are going away.

echo “$meaningOfLife”;

By far, this is the most common version of string interpolation. Just put the variable in a string with double quotes. If you are doing this, you are fine, this is one of the two ways that are staying.

echo “{$meaningOfLife}”;

echo “{$dogulasAdams->meaningOfLife()}”;

I always considered this way “old-skool”. Yeah, we used to do it way back in the day but I’ve not done it this way in a long time. Still this works, it’s clean, and it’s easy to understand. This is the other one that is staying.

This is also the only method that allows you to use object properties and methods. So if you want to use string interpolation with an object, you will need this method.

echo “${meaningOfLife}”;

This one is going away. Yes, it does the same thing as the first two, but it is a little more confusing because the $ is outside of the braces. 

$fourtyTwo = 42;

$meaningOfLife = ‘fourtyTwo’;

echo “${meaningOfLife}”;

Finally, we have the way that you can use “variable variables” from within string interpolation. This is just too many levels of indirection. In the code above, we eventually get to the point where we echo out 42, but we take the long way around. 

Starting in PHP 8.2, the last two structures will emit a DEPRECATION WARNING in your log files. In PHP 9.0, they will stop working altogether and cause your program to crash. (or throw an Error that you can catch, but probably can’t recover from.

Wrap Up

This is the first PHP 8.2 Release Candidate. Don’t play with it on any production site. If you want to test it with an existing site, set up a new site for testing, clone your production site into it, and play with that. When you are done, you can just delete it. 

As you poke around in your new testing environment, check your log files after every test. Make sure nothing fails and see if any new WARNINGS pop up. 

If PHP 8.2 is anything like PHP 8.0 and PHP 8.1, I don’t expect modern PHP code to have issues with it. Thankfully, Santa ElePHPant’s Elves that work for SiteGround make it incredibly easy for you to test things out to make sure your site can run as fast as possible with PHP 8.2

Speaking of performance, PHP 8.2 hasn’t been properly benchmarked yet, but we have come to expect every version of PHP to be a little faster than previous versions. With changes to the CSPRNG system and other things like removing the old libmysql, it’s a safe bet that this version will be faster than PHP 8.1.


While you are testing, cloning, and observing results, make sure you take time to tweet out a huge THANK YOU to Santa ELePHPant and all of the little ElePHPant Elves that made this release possible. Rumor has it that they keep an eye on twitter.com/@php_net

To celebrate the latest release candidate PHP 8.2, we are giving away 5 exclusive SiteGround PHP elephant plush toys (a.k.a Groundy) in a raffle, running from September 8, 2022 until September 11, 2022. Read more on Twitter.

[subscribe_cta]
Moving to a State-of-the-art, In-house Built Spam Protection Solution

email spam protection service

When you’re busy processing tons of emails each day, and we all are, the last thing you need is a bunch of spam messages sneaking into your inbox. Spam protection has always been an important part of our email service and in our strive to constantly improve it we are now introducing a new in-house built solution. It is designed to efficiently minimize the amount of SPAM emails delivered to your inbox, while constantly learning from your email reading behavior. It is also built specifically for our clients and works seamlessly as part of our hosting environment.

Efficient and easy to use for our clients

Less SPAM messages delivered to your inbox

Based on our multiple years of managing email services, we have created a system that decides with a high amount of accuracy which messages are legitimate and should reach your inbox, which are suspicious and should be delivered in your Junk folder, and which are outright dangerous and should not reach your email at all and will bounce instead.

Your email reading behavior trains the system

Your natural actions, while working with your mailbox will train the system. Whenever you move a message to or from your Junk folder you will improve its accuracy. Based on your action the system will add your personal perception of what is SPAM on top of its own underlying rules. Thus your feedback is taken into account seamlessly, without a need for you to use an additional SPAM management interface.

Easy interface to allow and block senders

And also, if you would like to tell the Spam protection system directly how to treat a certain sender, you can still use our easy interface to block or allow specific senders. By adding an email address or an entire domain to the Block or Allow List you indicate how you want this sender to be treated by the system. Check the following tutorial on how to use the Spam Protection service in Site Tools.

Better control and easier scalability for us

We may address our clients’ needs 

By using an in-house solution we can more easily address our clients’ specific needs and introduce new features and improvements faster. For example, we have noticed that the current setup makes it difficult for our users to find out when a legitimate email is not delivered to them and is marked as spam by the system. This happens because the message is placed in a quarantine folder in a separate tool that is not part of the user’s natural email management. With the new solution we were able to address this issue by using the much more visible Junk folder instead.

We may handle email usage spike better

When we manage the spam protection system as part of our own infrastructure, we can easily scale it. Even if there is a steep global increase in the email traffic we can seamlessly add the resources needed for the evaluation of the excessive messages. Thus the email delivery will not be delayed for our clients, regardless of the unexpected usage spike.

How to use SiteGround Spam Protection?

All SiteGround clients have our state-of-the-art Spam Protection features enabled by default.

[subscribe_cta]
November 2022 SiteGround Life Recap

November brought Black Friday, Thanksgiving, great employee events, and more awards.

What a great month November was! Can’t wait for December and the excitement of Year-end. If you want to learn more about life at SiteGround and our open positions, check careers.siteground.com.

New Email Migrator Tool for Fast and Easy Email Transfers

migrating email messages from one server to another

When changing your hosting provider, sometimes it is not only about moving your website and pointing your domain to the new server. If you also use email services as part of your hosting plan, the most challenging part of the process may be transfering your email accounts and messages without losing data or creating disruption to your business communication process. To address this challenge for people, who prefer to have everything hosted at one place, we have now added a new Email Migrator tool. It allows you to transfer your mail service from another server to our mail servers fast, easy and securely.

Why did we develop the Email Migrator

SiteGround clients who are transferring from other hosting providers already benefit from our automatic website transfer options. The Email Migrator tool streamlines this process even further, making the transfer of email services possible in just a few clicks, even by not so tech-savvy users. On top of that, the tool helps you keep your email communication intact and safely transfer all of it to our servers.

What are the benefits of our Email Migrator tool

In addition to making it easier to transfer your emails to SiteGround and have everything in one secure place, our Email Migrator has a couple of other added benefits:

  • Intuitive interface for easy migration start 🏗️

The tool interface guides you through the few steps needed to get the process started.

  • Secure and reliable transfer 🛡️

We’ll move your emails in a secure manner, ensuring privacy and data protection.

  • Fast migration 🚀

We’ve developed the tool in a way that the procedure won’t take too long. Yet, the exact time needed will depend on different factors, such as the size of the mailbox, remote server speed, and others.

  • Keeping the structure of the email account being migrated 📧

We’ll transfer your email account for you, including folders, messages and attachments.

  • No duplicates created 📑

We’ll make sure that there are no duplicates created during the migration process.

  • Automated process 🪄

There’s no manual work required on your end, as the migration happens in the background. You’ll need, though, to set up the systems that are beyond SiteGround control: point your MX records to make the new messages come to our server and reconfigure your email client to start receiving the messages from our server.

How to transfer your emails with the Email Migrator

To transfer your emails, you need to follow a few simple steps in your Site Tools > Email > Email Migrator. Read detailed instructions on how to transfer your emails and enjoy a hassle-free email migration to SiteGround!

The Email Migrator is basically the last piece of the puzzle that lets you have everything in one place. Transferring all things to SiteGround allows you to easily manage both your website and email in one account. Not only do you have everything in one place, but you’re counting on our proven expertise in both web hosting and email services.

[subscribe_cta]

Don’t Fall for Email Scams This Black Friday

phishing emails during Black Friday

The infrastructure that runs the Internet’s email hasn’t changed a whole lot in the past 30 years. Yes, we’ve layered a few things on top of it like Sender Policy Framework (SPF) and DomainKeys Identified Mail (DKIM) but at its heart, the protocol remains the same. That’s the problem. Email was designed in a simpler time. A time when the Internet was a trusted resource and nobody gave a second thought to the fact that it’s easy to say fudge the headers on an email so that it looks like your boss is getting an email from the President of the United States commending you for all your excellent work. I’m not saying that has happened or that I was a part of it…but hypothetically, it is possible.

So, if email can’t be trusted, what can we do? Well first, these days email is a lot more trustworthy. It is much easier to detect emails sent from someone, but say they are from the President, thanks to things like Sender Policy Framework (SPF) and DomainKeys Identified Mail (DKIM).

Even with these new technologies though, email scams are still rampant. As we charge headlong into the holiday season, let’s stop for a moment and look at a few things you can do to make sure you don’t fall for the latest scam. (Which is not sending emails to unsuspecting bosses…)

Email Scams You Need to Be Aware Of

Let’s take a look at a few of the many ways that bad people try to do bad things to you via email. This first group of scams all fall into the category of Phishing scams. A Phishing scam is basically an email designed to fool you into thinking it is from someone it is not and convince you to click on a link embedded in the email.

The Fake ‘’Account verification’’ Requests

These can seem to come from your bank, Netflix, Twitter, or one of those sites that you don’t admit to having an account on. It doesn’t matter where they are coming from, they all have the same basic message. 

“Your account has been locked for a REASON. To unlock your account before we delete it totally, click on this link.

Here’s a hint, no trusted system out there sends these emails out randomly. If you get one and you are not currently interacting with this organization, then it is almost assuredly a phishing scam.

When in doubt, pull out the paperwork you have for this organization, find a phone number and call them. Ask if there is a problem with your account. When they say no, thank them, wish them a great day, hang up, mark the email as spam, and move on with your life.

The unexpected ‘’Billing error’’ notifications

Did you know that it is possible for bad people to figure things out about you without you telling them? It is relatively simple to find out where a website is hosted. When bad people find out information like this, they like to use it for their gain and your loss. Such is the “Billing Error” notice.  

For instance, if you are a SiteGround customer and you get an email from SiteGround notifying you that there has been a billing error and you now owe $XXXXX more, stop. Don’t click any links in the email. Instead, go to the SiteGround support page and start a chat session with one of their great support people. They can tell you if there’s an issue with your account or not. 

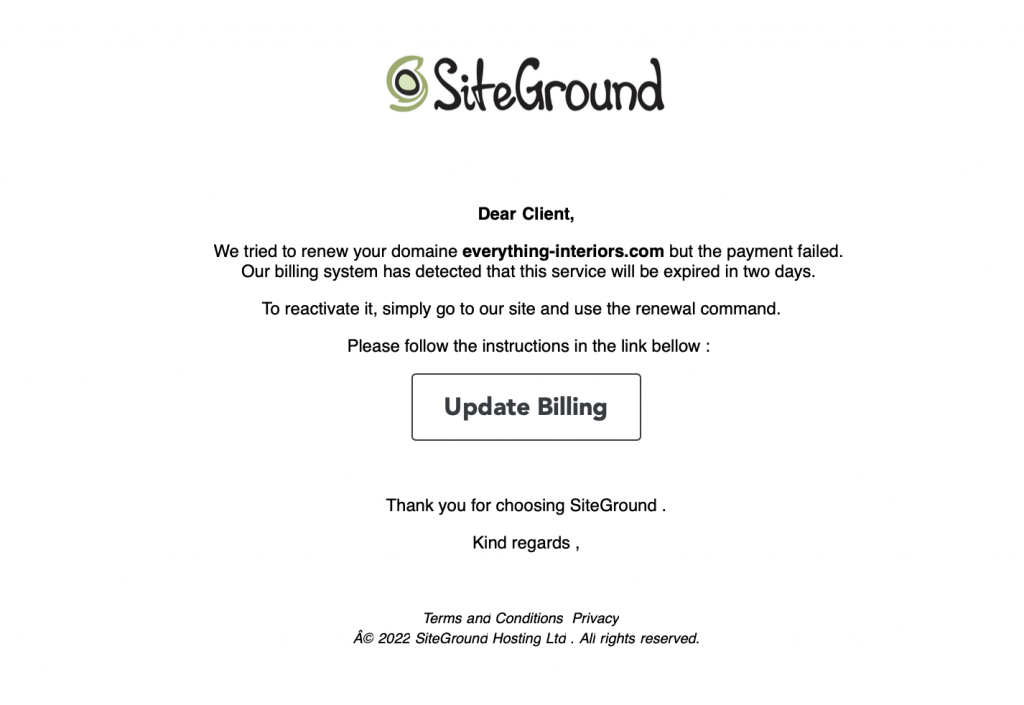
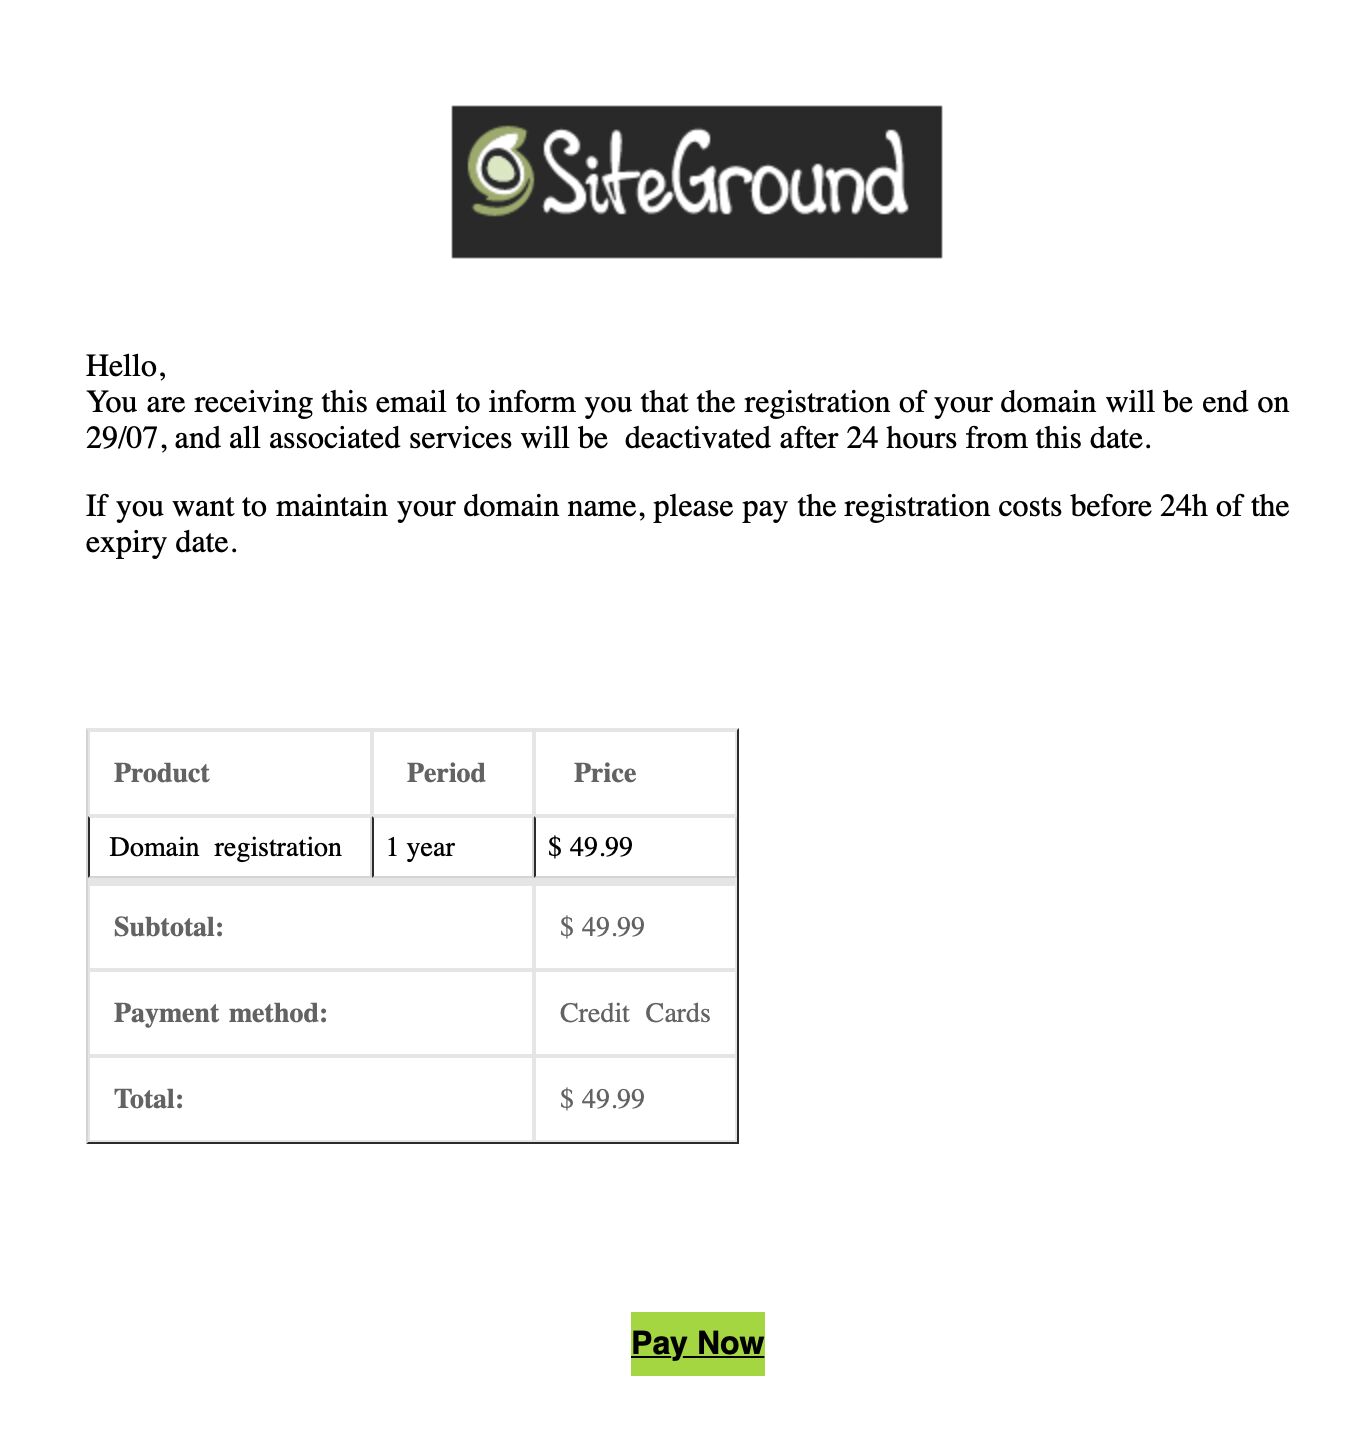
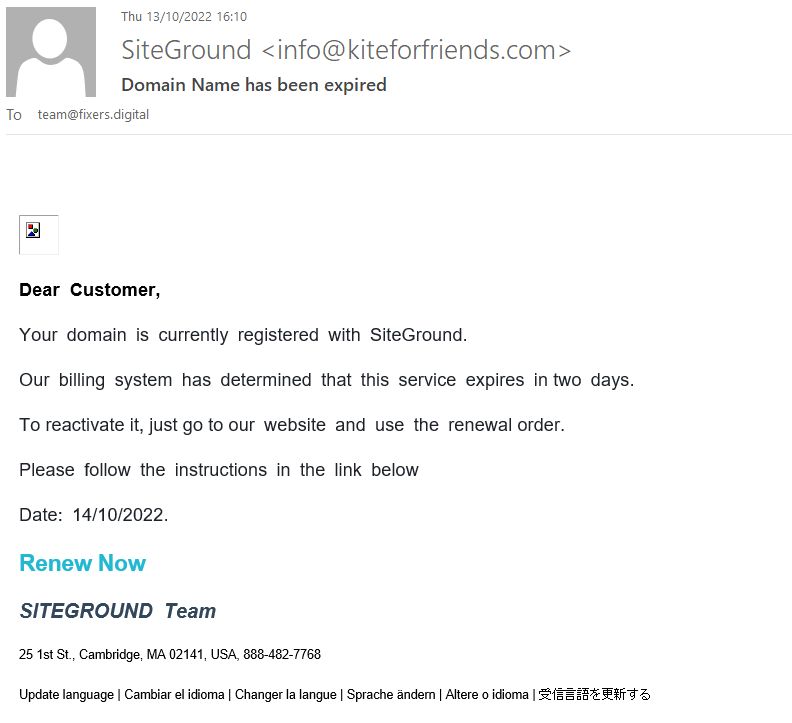
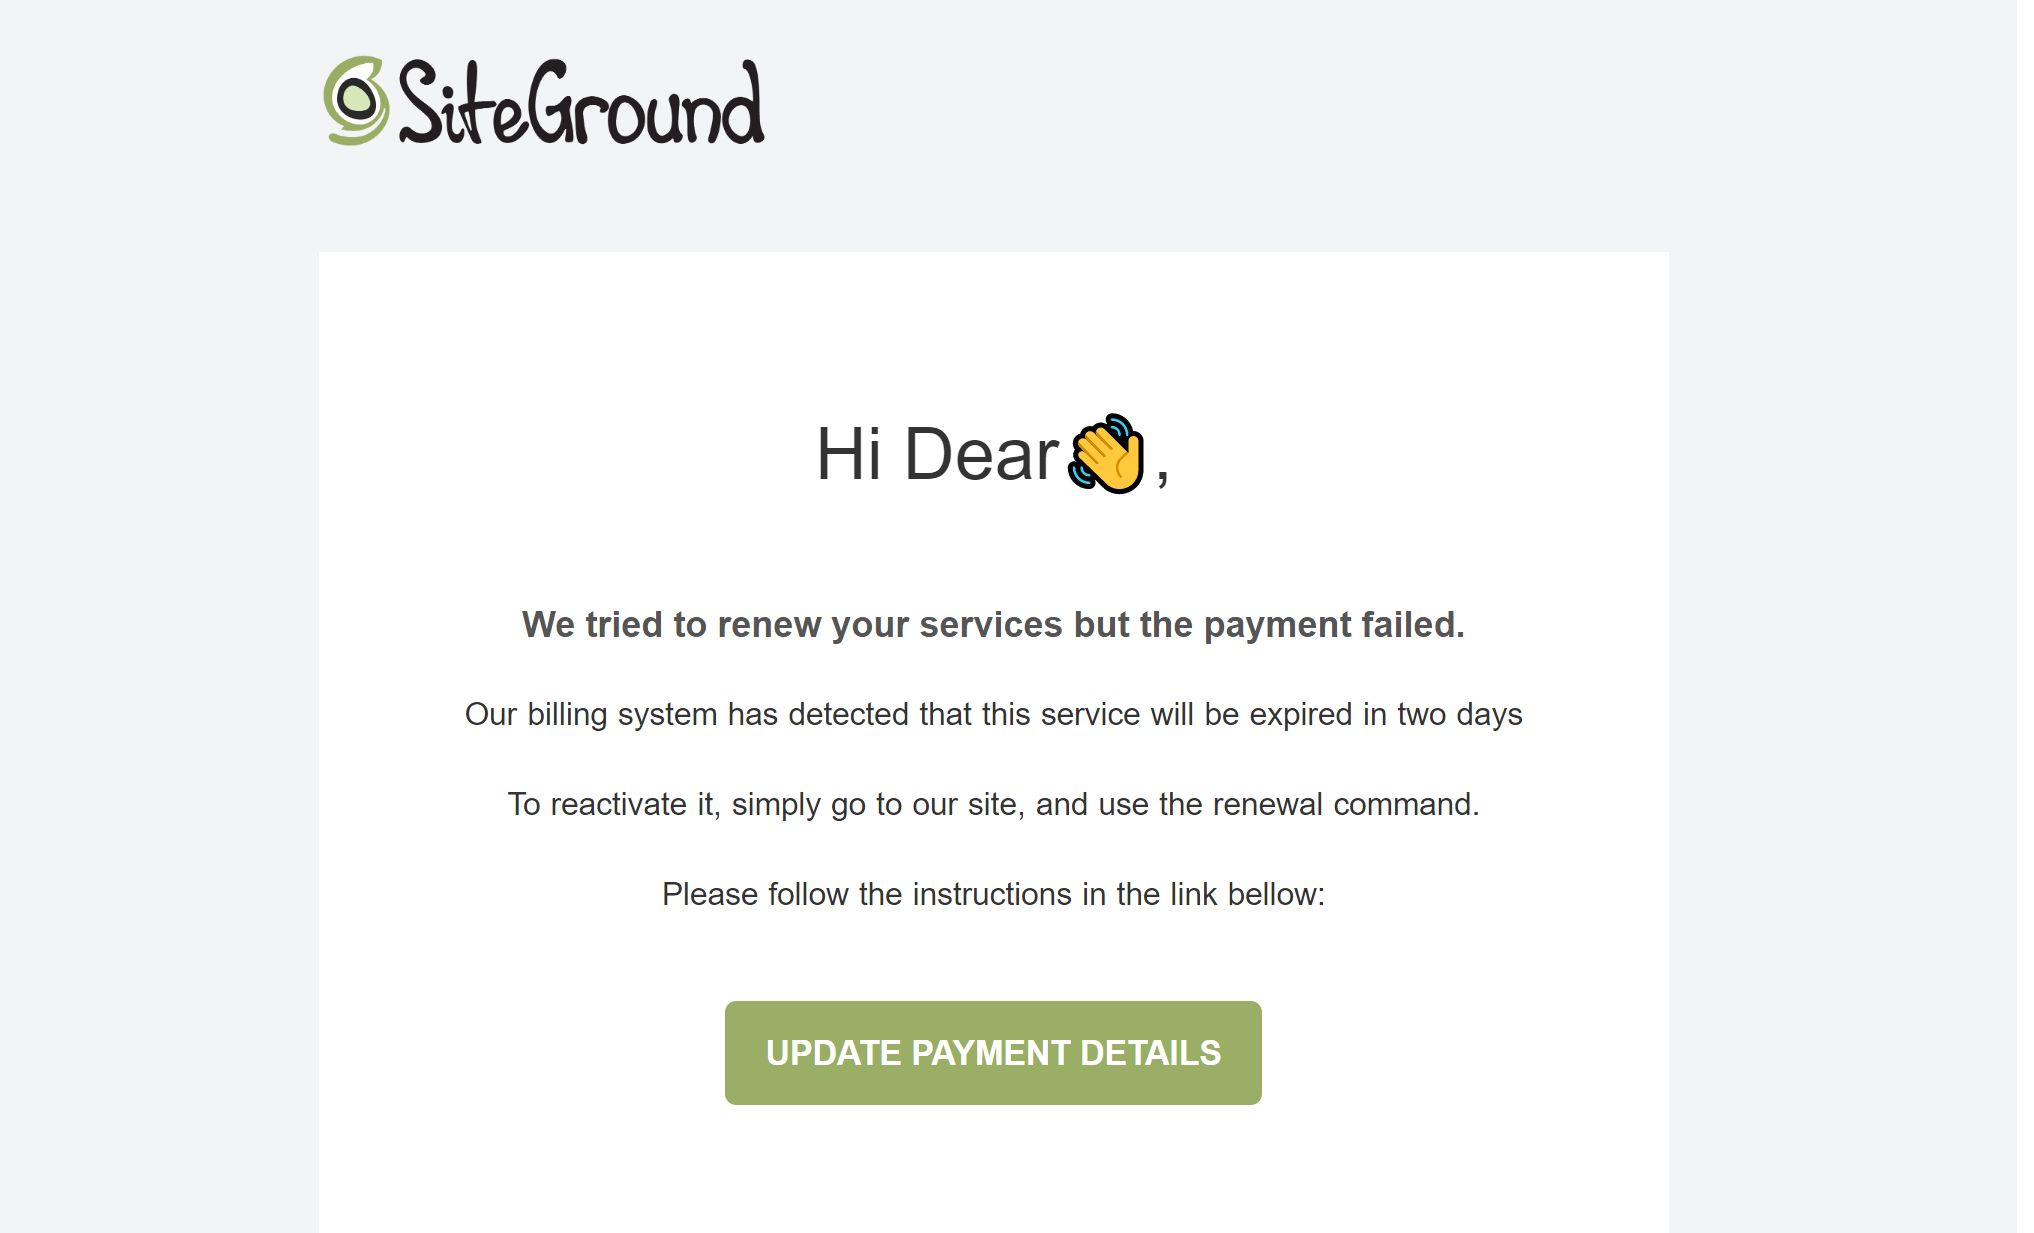
Here’s an example of a phishing email that requests from a SiteGround customer to update their billing details in order to be able to renew their domain:

Scam email example

Notice that this fake email does not contain the name of the recipient, and SiteGround original emails should include the name you’ve used for registering your account. 

Next, notice that this email has grammar and spelling mistakes. These are red flags for a scam email along with the poor formatting. 

Finally, the signature is not the one used by the SiteGround team. 

When you confirm that there is not actually a billing error, thank the nice support person, wish them a wonderful day, disconnect, mark the email as spam, and move on with your life.

The ‘’Order confirmation’’ requests

An oldie but a goodie – and one that pops up a lot these days because ecommerce has exploded – is the “Order Confirmation” email. These are most effective when they are from companies that you’ve never dealt with. They usually involve large sums of money as well. The idea here is to alarm you so much that you will obviously click the link to “Unconfirm” the order. 

If the email looks like it is from a company you don’t do business with, ignore it. Mark it as spam, and move on with your life.

If it looks like it is from a company you do or have done business with, contact them directly outside of the email. Talk with the sales or accounting department and see if someone has placed an order on your behalf… When you find that the answer is no…well, you know the drill by now.

The ‘’Click and collect’’ scam

Thanks to the recent pandemic, “Click and Collect” has become a common way to shop. You buy something online from a nearby retailer. You drive to their store and let them know you are there, they bring the item out to your car. Sometimes, they even put it in your trunk so you don’t have to even meet them face to face.

Nowhere in the Click and Collect workflow is there an email that says “Click here if you didn’t order this.” Treat these the same as Order Confirmation requests. If you don’t deal with the company, it’s a scam. If you deal with the company but haven’t placed an order, it’s a scam. If you are in doubt, contact the company directly, not by replying to the questionable email.

Sometimes, scammers are really REALLY good. They send you an email that looks exactly right.

Real Life Phishing Emails (Well, Screenshots)

What do good phishing emails look like? Here are a few examples of actual phishing scam emails sent to SiteGround customers.

Apart from all the red flags already covered above, the ‘from’ email address of these emails is not a valid SiteGround email. What is more, a proper SiteGround email would never mention the payment method used by you to pay for the service in question.

If you’re a SiteGround customer who comes to report such emails, SiteGround would ask you to send the whole email as an attachment, as they use it to train their own systems to block such emails (in case your email is hosted with SiteGround), so that they do not reach your inbox. In case your email is not hosted with SiteGround, you can mark it as spam in your email provider.

To learn more about how to stay safe from phishing email attacks, check out the blog post on this topic.

How Do You Stay Safe from Email Scams During the Holidays?

So how would you tell if this was a scam email? Well the easy answer is to “practice safe email”. Here are a few of the things I do before I click a link on an email, any email.

  1. Check the ‘from’ address.
    We’ve already done this but so very many phishing emails come from implausible email addresses. Most scammers don’t bother to try and hide it because so few people pay attention. A recent phishing attempt sent to me purported to come from NetFlix. However, the email address was XXX@yahoo.jp. Yes, Yahoo has a Japan domain but they don’t send email for NetFlix from it! Not even to Japanese customers.

    A good rule of thumb is if you were not expecting an email from someone, even a family member or friend, treat it as suspicious until you know it was actually from them. If you don’t recognize the person it came from, then automatically assume it is malicious until you can prove otherwise. 
  2. Check all links before clicking.
    Most email clients these days will let you hover over a link that says “Click Here” (or wherever) and see what the actual URL is. Read it VERY CAREFULLY. Pay attention to the domain name. https://goog.le is not the same as https://google.com. Read it carefully. If it looks suspicious, do not click it.

    Some email programs will show you the link in a popup when you click it and ask for verification before it actually opens a browser to that link. If your email program will do this, by all means turn this feature on. Yes, it adds an extra step before you can see that precious baby picture your friend sent you, but it allows you to make sure that you are actually going to see a baby picture and not install malware on your computer.
  3. Do not automatically download attachments
    Your email program should be set to not automatically download attachments. This means that if you download something from an email, you will have to do it on purpose. If the email doesn’t seem right or fails any of the checks we’ve discussed here, don’t download anything. Even things like Microsoft Word documents which seem innocuous (click here to see the invoice for the service you didn’t order) can do malicious things if you open them. If you weren’t expecting someone to send you an email attachment, don’t open it!
  4. Read The Headers
    Ok, this is for the hardcore email nerds out there but those of us who have been doing this a while can discover a lot by reading the headers that come with every email. These days email programs hide the headers from you but they are there if you want to read them. 
  5. Listen to your gut
    My wife, The lovely and talented Kathy, got an email from our worship pastor one day with the subject line “I love you”. She was good friends with this man and while the subject line confused her, it also piqued her interest. She opened it only to find that there was a malicious script attached to the email. It deleted about ½ of the images we had stored on our home server before I could stop it. Thankfully, I had a backup so there was no loss, other than the hours it took to clean up the mess. Had she simply called him, opened a new email and written him at the address she had in her contacts list, or contacted him in any of a half-dozen other ways, she could have found out that it was not from him but was a scam. Instead of trusting her gut, she opened the email.

Other Black Friday Scams To Be Aware Of

Email is by far the easiest way for bad actors to get unsuspecting people to do bad things. However, there are a couple of other ways.

If you get an email with a link to goog.le, it’s easy enough to spot. However, if you are doing your shopping at https://reallyLongDomainName.com and you misspell it or “fat finger” it (typo), then you might end up at a site that looks exactly like the one you were aiming for.

Bad actors look for common misspellings for profitable domains. They buy them up and put copycat sites up. These are sites that look just like the one you were looking for. They probably even have products and a shopping cart. However, make no mistake, they are scams. When you put in your personal information and credit card number, you are not going to get those purple widgets you ordered that your sister will just love. You won’t get anything but a nasty surprise when your credit card statement arrives.

This is really easy to thwart, if you pay attention.

First, after you arrive at a site, look at the address bar. Is there a little lock next to the domain name?

The little lock means that the domain you are using has a secure certificate and that it is valid. If you don’t have a little lock, or if there is a line through it, that means that either the certificate does not exist, or that it is invalid for that domain. Both of those are really big red flags that you don’t want to do any business on this site or put in any of your personal information.

A SSL certificate isn’t always enough to prove that you are on the right website. Scammers can register sitegroound.com, for example, and install a certificate on it. The certificate just provides encryption in most cases. It’s always a good idea to also double check the URL address, especially when you make payments, create accounts, fill out forms, etc.

Sites impersonating landing or login pages

The final type of website scam we’ll talk about are fake login pages. These might be part of a very good looking fake, or you might arrive at a site only to find that before you can get to the good stuff, you have to enter your login credentials. If this is an ecommerce vendor you normally do business with, or an institution you bank with, stop. Don’t do anything else. Sites like that don’t just put up a login page without letting everyone know well in advance. These are nothing more than “password collectors”. 

If you do enter your credentials into the site, they won’t work…because they are fake. But humans are stubborn. You will assume that you mis-typed something…especially if you are using a long and very secure password. So you’ll try again.

If you are like most of us, when it doesn’t work the second time, you will assume that you’ve used the wrong password and you’ll try another password, and another, and maybe even a 4th one before starting to think that something may be wrong.

Every set of credentials you entered have gone into a database and bad people will start using them to try and sign in to any site they think you may have an account on. Since you were giving them real login credentials, you’ve given away the keys to the kingdom.

Be watchful, be alert, be suspicious bordering on paranoid. Make sure before you put any information into a website, you are absolutely sure you are at the right website. Looks can be deceiving.

How to Practice Safe Internetting This Holiday Season

  1. Always be suspicious of unknown or unexpected emails.
    If you don’t know the person, or even if you do know them but aren’t expecting to hear from them, be suspicious. Yes, your long lost aunt may be contacting you via email with a hotmail.com email address to tell you that she’s leaving you her entire fortune when she dies and she needs you to sign the will, but chances are really good that it might NOT be her. Verify before you take any action.
  2. Don’t click a link in an email until you are absolutely sure you know where it is going and what is going to happen.
  3. Don’t provide your personal information to any site unless you are positive and you know that it is the site you think it is. If you don’t think you are on the right site, close the browser immediately.
  4. Whenever possible, use a Virtual Private Network (VPN) from a reputable provider.
    I won’t name my Internet provider but I will say that I do not trust them. They have been known to make it easy for bad people to watch the traffic going across their network and pull out information as they see it. These days almost all websites use encryption to make sure that’s not easily done, but it is still possible for people with enough time, money, and determination. So whenever possible, I use a VPN to encrypt my traffic even further.

    VPN software isn’t expensive these days, as a matter of fact, if you are a “computer person” you can download, configure, and run your own. I don’t recommend that as it’s easy to get it wrong, but I’ll admit to having done that in the past. These days, I use a commercial VPN that comes with my virus protection. Now, my neighbor can’t see any of my traffic because I’ve got an encrypted tunnel between my network and a server in Miami, FL, USA. (I can choose from about 50)
  5. Don’t use the same password on any 2 websites
    Look, I know how hard this is. It’s difficult to come up with one secure password that you can remember, let alone the 20-30 you need to make sure every site is different. I suggest using a password manager from a reputable software company. There are a few of them out there. The one I use works on Windows, Mac, iOS, iPadOS, and Android. So, no matter where I am at, my passwords are with me. All my passwords on all major sites are long, random, and unique. If you know one of them, you can’t get into anything but that one service I use it for.

Wrap-up

Stay safe out there this holiday season. Have fun, enjoy the company of family, and if you get an email from me saying that Bill Gates is giving 1 Bitcoin to each person that forwards this email…well, you get the idea.

[subscribe_cta]

Journey of an Online Buyer 2022 (Free Guide)

Journey of an Online Buyer Guide

This blog post outlines SiteGround’s Journey of an Online Buyer infographic. Download the full guide to learn about the shifts in customer behavior and how to prepare your website for them. 

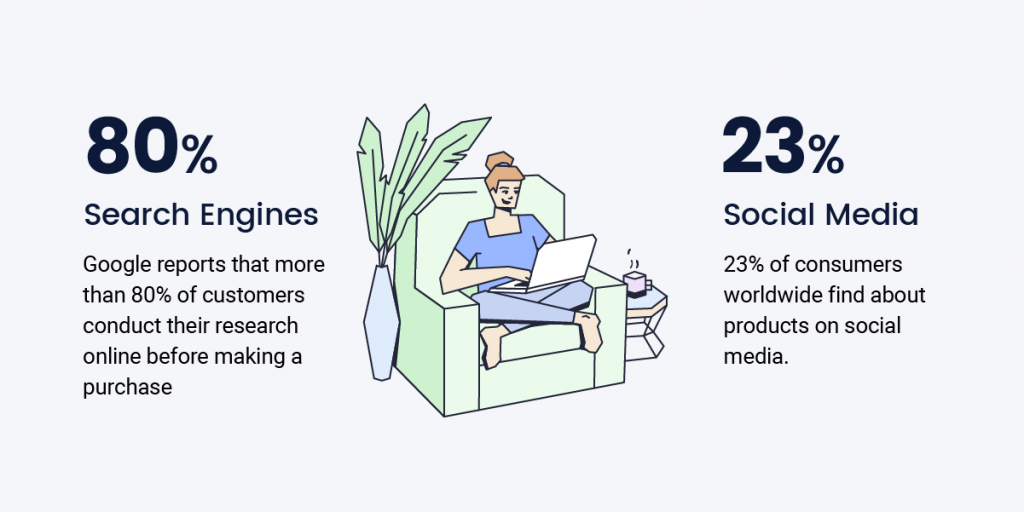
With consumers changing the way they shop, have you changed the way you sell? Buyers today are more informed, involved, and connected than ever before. And in today’s digital landscape, the buyer’s journey has taken on new shapes and forms. It is no longer a linear process but a complicated web of touchpoints and interactions. To keep ahead of the competition as a small business and website owner, it’s critical to grasp this new buyer’s journey online.

What is the buyer’s journey?

The buyer’s journey is the process consumers go through, from initial awareness to final purchase. It illustrates how each step leads to the next to ensure you are aware of the actions that cause potential clients to either make a purchase, or back out of it. By understanding the buyer’s journey, you can better anticipate the needs of your customers and provide them with a seamless experience from start to finish.

The three stages of the buyer’s journey

It’s up to you to observe how potential buyers react to your selling approach and determine precisely where to focus your marketing and sales efforts. The buyer’s journey is mapped out in three stages. Each stage allows for distinct interactions between you and your users. 

Awareness stage

During the awareness stage, the buyer becomes aware of a problem or challenge they face. They will then begin to search for solutions to that problem. Your job during this stage is to make sure you are visible to the buyer and that they are aware of your product as a solution to their problem.

Consideration stage

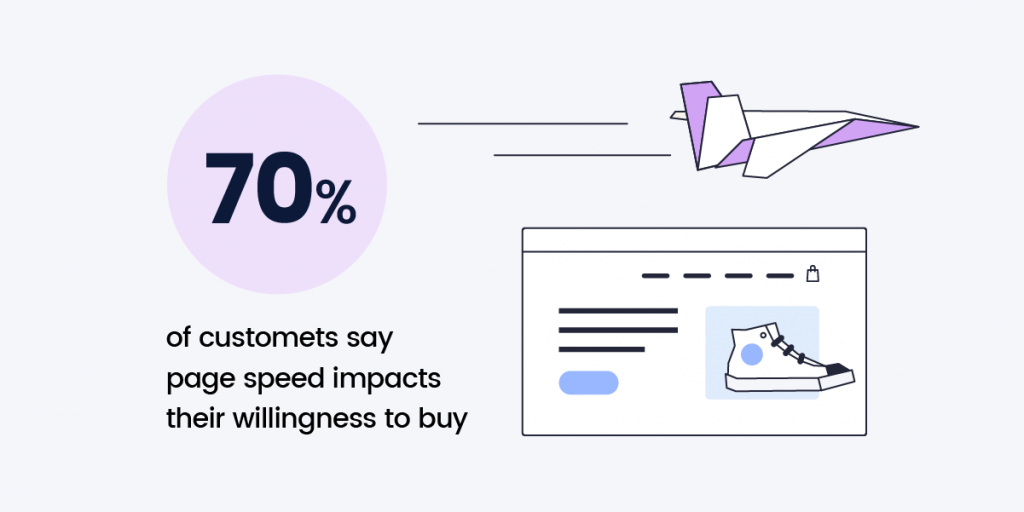
The consideration stage is when the buyer narrows their options and compares different solutions. Usually, this happens on your website. During this phase, it is your responsibility to give the customer the best user experience possible, which entails having a fast and secure website. Also, give them more information about your product and how it compares to competing products.

Decision stage

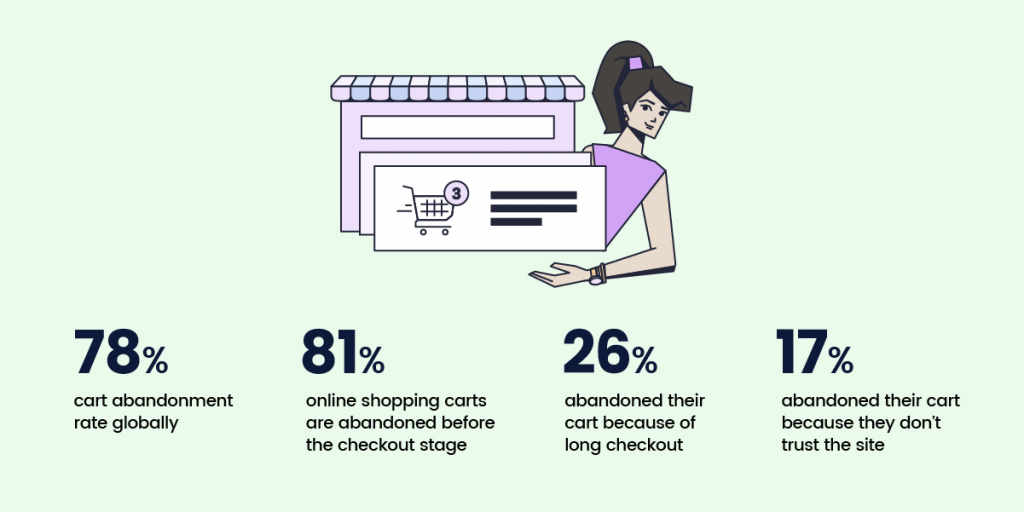
The decision stage is when the buyer finally chooses a solution. Your job during this stage is to make the purchase process as easy as possible and address any final buyer concerns.

Your website’s role in the buyer’s journey

While the buyer’s journey may start elsewhere, such as with a Google search, a large part of it will happen on your website. This is why it’s essential to have a website optimized for SEO that provides a great user experience, including ultrafast website speed, security, and reliability. If you can do this, you’ll be able to guide the buyer through the journey and ultimately convert them into a customer.

The 2022 online buyer’s journey highlights

Online shopping has evolved beyond simply being more convenient

Online shopping has come a long way since its inception. What started out as a convenient way to search for items has evolved into a major part of the retail landscape. Consumers around the world were once skeptical about online shopping, but that has changed dramatically over time – especially after the pandemic. Statista reports that in 2021, retail ecommerce sales were 5.2 trillion US dollars globally. They estimate this number will grow 56% in the next years, amounting to 8.1 trillion by 2026.

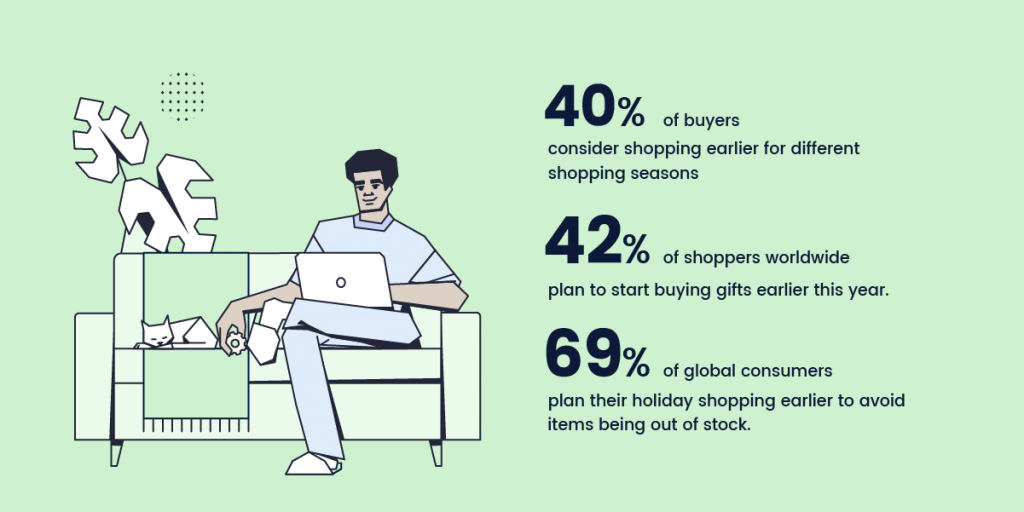
Seasonal shopping now starts much earlier 

In the past, people would wait until the last minute to do their holiday shopping. However, people now do their seasonal shopping much earlier. They have many more options to choose from online, and want to take their time to find the perfect purchase. This is due to several factors, one of which is the growth of online shopping. With the shopping season starting earlier and earlier each year, small business owners need to be prepared to accommodate early shoppers.

As advertising costs soar, brands prioritize building customer lifetime value

Building customer lifetime value is more important than ever. As advertising costs rise, brands are increasingly focused on creating long-term relationships with their customers. And that’s okay because we’re also seeing a shift in the way consumers choose from whom to buy. They’re much more likely now to purchase from companies with strong brands that identify with their consumers. It’s important to remember that sustainable growth comes from focusing on your customers. So you need to build a brand that customers can trust and foster a sense of community. 

Download the full guide below to explore the changes in customer behavior and learn how to get your website visitors a step closer to the “buy” button on every step of their online journey.

>> DOWNLOAD THE FULL GUIDE 

[subscribe_cta]

How to avoid bad bot traffic during Black Friday

bots attacking a browser and finally cracking it

Last week, we helped you get your website ready for the Black Friday traffic spikes. Now that you’re all set to handle the upcoming traffic, do you know how much of it is real and how much – non-human? According to Statista, in 2022 more than 40% of Internet traffic is from bots, and a significant portion of that is bad bot traffic. This kind of bot traffic hurts your online business and can lead to both financial and conversion losses. Let’s dig deeper into what bot traffic is, why most of it is so harmful, and how to avoid it during the busiest time of the year.

What is bot traffic and why it should be cut down to a minimum

Bot traffic is any non-human traffic that comes to a website or app. Some of it is good, when it originates from SEO crawlers (such as Google crawl bot), commercial, site-monitoring, or feed bots. Needless to say, all of these cause no harm to your site. On the other hand, bad bots come with malicious intent. These can leave spam comments, irrelevant backlinks, weird advertisements, collect private information, reuse your content, perform DDoS attacks, and other malicious activities.

How bad bot traffic affects your website

Bad bot traffic may have different consequences on your website and business, causing multiple damages:

  • Website security and availability damage

Bad bot traffic hurts your website security and availability. For instance, these massive amounts of traffic to your site are a way for hackers to cause a DDoS attack. During such an attack, the traffic is so massive that the server where your site is hosted cannot handle it. This can make your website slow, unreliable or even unavailable for your users. 

Bad bots are also the main force of a brute-force attack – a way to guess your password/login details by trying numerous combinations of letters, numbers and symbols. If such an attack is successful, malicious hackers gain access to your account and/or private information.

  • Website speed issues

Even if it doesn’t cause massive hacker attacks, bad bots activity can make your website much slower or even unavailable for your real visitors, affecting their overall user experience. To have your visitors stay longer on your site and turn them into clients, you’d want them to have an excellent user experience. A huge part of that is your website loading speed being as fast as possible.

  • Analytics metrics and SEO rankings chaos

Bad bot traffic can also hurt your analytics metrics and SEO rankings. For example, too much bad bot traffic can bring your site down and cause 503 errors (“site is temporarily unavailable”). This directly negatively impacts your SEO rankings. What is more, bad bots can affect your analytics metrics, causing abnormally high pageviews and bounce rates, sudden drop/increase in session durations, and fake conversions. All these factors may confuse you as a site owner and you may not be able to make sense of your analytics data.

How we decrease bad bot traffic at SiteGround

At SiteGround we take multiple measures at different levels to reduce bad bot activity by default for the websites hosted on our servers, so you can have peace of mind.

Improved and advanced AI anti-bot system

Our AI anti-bot system has successfully been blocking millions of brute-force attempts per day. Recently, we improved it even further, resulting in 95% less bad traffic. Its core features are still there – analyzing and recognizing traffic patterns to eventually stop brute-force attempts. With each new brute-force attempt, the system’s knowledge expands and it gets better at preventing future attacks. As of recently, we’ve upgraded the system with a traffic validation feature that stops even more malicious non-human bots by minimizing the number of brute-force attacks. Currently, the system blocks a huge percentage of bad bots traffic towards our servers, allowing more capacity for your websites for legitimate traffic.

Combined with our enterprise-grade security system, these server-level security optimizations block the majority of all bad bot traffic and ensure website protection on a global scale. Let the numbers speak for themselves – 99,99% of bad traffic is blocked before it even reaches your website.

Smart, server-level WAF

Hacker attacks usually increase during the Black Friday season. A single outdated WordPress plugin, theme, or vulnerability can easily be used for massive damages during this busiest time of the year. That’s where our smart Web Application Firewall comes to the rescue. Our security experts closely monitor security bulletins and server activity 24/7, and in case of reported exploits, immediately add custom WAF rules (patches) into our server firewall to protect your site from current hacks and breaches due to outdated plugins, and other vulnerabilities. Our proactive security approach allows us to react much faster, often before the original plugin, theme or app developers have had the chance to release an official update. The most recent example of this was just last month, with two previous major ones not so far behind – a plugin vulnerability patched on day 0, and a Linux Kernel vulnerability patched within hours of detection.

DDoS protection

To address potential DDoS attacks from bad bots, we have a system of hardware and software mechanisms to protect your sites:

  • A hardware firewall that filters flooding traffic;
  • A local software firewall with more complex functions and traffic monitoring;
  • А limit to the number of connections a remote host can establish;
  • A check for a high number of failed login attempts from hosts and filtering them, if any.

24/7 server monitoring system

Again, in addition to all monitoring and prevention systems and checks in place, our expert system administrators team are monitoring our servers 24/7 for any system issues and in case of any, can react quickly to save the day.

How to identify that you have bad bot traffic coming to your site

Now, you probably wonder what are some signs and symptoms of bad bot traffic that will help you identify whether your site is in danger. Here are some of the red flags and ways to prevent them:

  • Check your site traffic stats

You also need to check your traffic statistics, especially the IP addresses and the sources of traffic. For example, regular and high number of visits from the same IP address or increase in traffic from other regions or countries, from which you didn’t have (much) traffic before, could be an indication of bad bot traffic. As a SiteGround customer, you can easily check your traffic statistics in Site Tools > Statistics > Traffic.

  • Keep an eye for unusual users’ behavior

Remember to monitor your users’ behavior regularly. In case there are increased spam comments under your posts, strange user registrations, and/or increased blocked login attempts, these are all red flags that you might be getting bad bot traffic to your site. WordPress users, who have the free SiteGround Security plugin installed, can monitor their site and login page for unauthorized visits and brute-force attempts from their Activity Log menu. What is more, they can easily block suspicious IPs and visitors.

  • Make regular speed tests

You probably already do that, but if you don’t, it’s a good idea to start making regular website speed tests. For this purpose, you can use a number of different tools to measure your site speed, such as Google PageSpeed Insights, Pingdom, GTMetrix, and others that generate results in all the major speed metrics. 

In case you have the free SiteGround Optimizer plugin installed on your WordPress website, you can run a speed test within the plugin in its Speed test functionality. The check uses Google PageSpeed, provides information on the level of optimization in over 20 different areas, and gives you optimization suggestions.

If you identify that your site is experiencing page loading speed issues, dig deeper into the problem to find out the causes. These might not necessarily be bad bot traffic issues, but that’s one of the main potential reasons behind the slow speed results.

How to filter bad bot traffic yourself on SiteGround

Some of the traffic that reaches your websites may seem legitimate, even if it’s not. Thankfully, there are a number of ways and free services we offer to let you filter good from bad website traffic all by yourself:

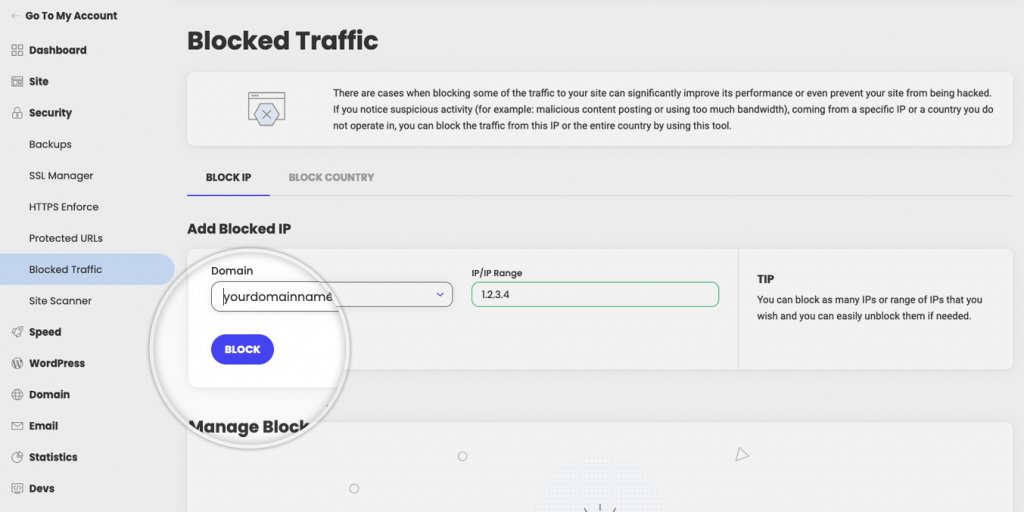
Both options allow you to easily block suspicious or malicious traffic to your website. If you want to block a specific IP address from accessing your site, because, for example, you see it’s using too much bandwidth, you simply go to Site Tools > Security > Block Traffic, choose the domain for which you want to block access, then add the IP address (or a whole range in IP/IP Range), and finally click ‘Block’.

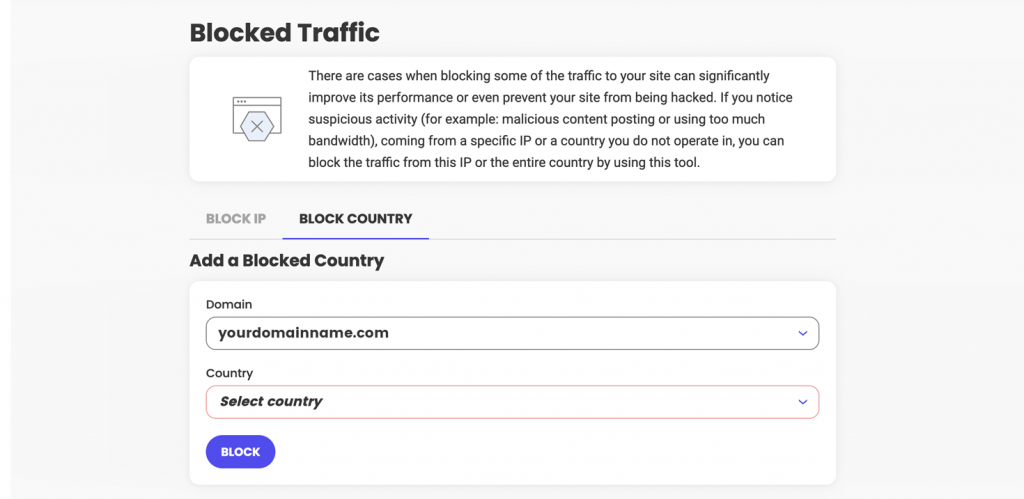
Similarly, if you notice that you get suspicious abnormal activity from a country you don’t usually operate in or have clients from, you can easily block traffic from it in a few clicks. You need to go to Site Tools > Security > Block Traffic > Block Country. There, you choose the domain for which you want to block access, pick the desired country to block in the Country dropdown, and finally click ‘Block’.

These two options will help you not only block bad bot traffic coming to your site, but they can also significantly improve your site performance by reducing the unwanted traffic and giving your site more capacity to handle real human traffic.

Improving your site capacity to handle more requests

In case you’ve identified that your site still gets some bad bot traffic which cannot be easily filtered or removed, you can decrease its negative impact by improving your website speed and performance, which will allow more capacity to handle any type of traffic altogether. Here’s how to do that:

We’ve developed a powerful caching system to help you cache as much content on your website as possible. Cached content is served much faster to visitors and thus improves your site capacity to handle traffic. Our system is comprised of three caching options that are all available in your Site Tools > Speed > Caching: NGINX Direct Delivery for caching static content, such as images and CSS files; Dynamic Caching for dynamic content to be stored in the server RAM, and Memcached for storing data and objects in memory (best for database-driven websites).

  • Use our other optimization services

We do a lot to improve website performance and you can make use of our premium solutions. Here are three of the main ones that can speed up your website and make room for more visitors’ requests. 

Our in-house developed SiteGround CDN requires no configuration, it’s easy-to-manage with just a few clicks, and above all, makes your site load blazingly-fast for visitors around the world. Its Basic version comes completely free of charge and provides your site with all the essential features to handle international traffic from various international locations.

Another in-house developed speed tool is the free SiteGround Optimizer plugin for WordPress websites. It provides you with many different optimization options (media, frontend, environment) that can all be enabled in a few clicks.

Last, but not least, our unique ultrafast PHP setup makes your pages load up to 30% faster and allows the server to process your website’s visits quicker.

Wrap-up

While most people are busy selling and buying goods and services during the Black Friday period, bad bots are also more active than ever, “visiting” websites and causing all kinds of potential issues. If not addressed on time and in the proper manner, they can ruin a big chunk of your holiday conversions during that time of the year, when you worked hard to get the highest number of sales.

[subscribe_cta]

October 2022 SiteGround Life Recap

Fall is here that brought lots of pumpkins, smiles, great talks and events at SiteGround.

  • SiteGround Brand Gurdian, Dima Peteva, got invited to talk about advertising on podcasts and also gave a keynote at the Future of Work conference about how to think like a start up in a big company and grow through talented people
  • The HR team was really busy this October:
  • Traditionally, we support the Sofia OpenFest and open source community. This year, SiteGround was one of the biggest sponsors, had 2 speakers and a booth where we met great people
  • Back in April, we went and planted a forest in Vitosha mountain. This means that over the next few years, we need to occasionally go to take care of it. In October, we went to check on it and prepare for the cold winter and were so happy to see that most of the trees have grown through the summer
  • Another open source community we are great supporters of is the WordPress one and this month we hosted a meetup in Plovdiv and attended WordCamp Valencia
  • Our team also attended TarugoConf in Madrid
  • At SiteGround, each team gets the opportunity to attend conferences to hear and learn about new ideas, network with the top professionals in a specific field. Our System Test Engineer Team attended PostgreSQL Conf in Berlin
  • SiteGround CEO, Nikolay Todorov, got invited as panalist to the Digital Trends 2022 Conference
  • October was Cyber Security Month, and Daniel Kanchev, Product Development Manager, gave a webinar on how to bullet proof your site security
  • At SiteGround, we take sport and wellness seriously, and employees (and their kids!) took part in the Sofia Morning Run
  • And at the end of the month, our offices got spooky as we celebrated Halloween.

What a great month! If you want to join the fun and growth, learn more at careers.siteground.com.

Ivo Tzenov and Tenko Nikolov are Leaders of the Bulgarian National Revival 2022

The two SiteGround entrepreneurs foundation will be called “Lead by example” 

Ivo Tzenov, founder, and Tenko Nikolov, CEO, of the leading Bulgarian IT company SiteGround are among the ten Leaders of the Bulgarian National Revival – the public campaign of the Bulgarian National Radio, which each year distinguish ten people who inspired those around them, created change and did good through the year.

In the video, Tzenov and Nikolov, explained  about their social activities during the years, vision regarding the development of the foundation to support Bulgarian sports, healthcare and education. If you think their mission is close to your values ​​and deserves your vote, support them by voting HERE.

A team of journalists from the Bulgaria National Radio nominated the most outstanding persons and projects in the past year, and the public radio listeners sent in nominations for their Leaders of the Bulgarian National Revival for three weeks. Among all the nominees, more than 200 applications – a jury consisting of Prof. Ognyan Gerdzhikov, Dr. Rumen Manov, Svetoslav Ivanov, Daniel Nenchev, Eleonora Gadjeva, Dobrina Cheshmedzhieva and Iva Doichinova determined the ten names that marked the year 2022 with their awakening activity.

“SiteGround has been supporting various educational and social initiatives for years, so the decision came naturally to establish our own foundation, which will be called “Lead by example” and will work in the field of health care, education and sports”, commented Tenko Nikolov and Ivo Tzenov.

Until now, SiteGround is among the largest investors in Bulgarian education. In 2021, the company supports the “Tеch for Bulgaria” foundation with BGN 20,000, and from 2022 the commitment is worth BGN 100,000 over a period of three years, or a total of BGN 300,000. The company will donate BGN 12 million to the first Bulgarian Institute for Computer Sciences, Artificial Intelligence and Technologies (INSAIT) within five years. The amount will cover the costs of remuneration of the world-class scientists that the institute will attract to teach in our country, for a period of five years. SiteGround is among the biggest investors, along with the Bulgarian government and tech giants like Google and Amazon.

SiteGround has also donated to various NGOs that support career guidance for young people as well as entrepreneurial projects and mentoring.

Your Website’s Essential Security Features. Are They On?

essential website security features

Building and maintaining a strong website security is a constant process that often gets neglected by website owners due to its complexity, time consumption and cost. As a hosting provider, we know better. Over 18 years of experience in hosting, maintaining and securing millions of websites has taught us that website security is absolutely critical for every online business. We have seen the devastating consequences a hack can have on a website and ultimately on a business, and we have dedicated serious efforts to preventing and minimizing the effects of hack attempts. 

Over the years, we have optimized the security of our platform by developing sophisticated security systems, introducing a variety of security tools, plugins and features, and constantly analyzing and monitoring traffic and patterns to recognize potential threats. While all of this has made us one of the most secure and trusted web hosting providers in the world, we know that platform security on its own, is not enough. The involvement of webmasters and site owners is just as important for properly securing a website. That is why we have compiled a list of the most essential security features you can enable that can make the difference between a hacked website and peace of mind.

Use SSL

Today an SSL is absolutely essential for every website. An SSL certificate encrypts the connection between your visitors’ browsers and your website’s server so that the data transmitted between the two, such as personal information, credit card data, login credentials or else, cannot be hijacked by hackers. 

SiteGround clients get free Standard and Wildcard SSL certificates with all hosting plans, regardless of the number of sites. Make sure you have your SSL installed and traffic properly redirected via HTTPS from Site Tools > Security > SSL to ensure the encryption of the connection. 

If you have a business website or you’re processing online payments, you may consider our premium Wildcard certificates that come with $10,000 underwritten warranty and a dynamic site seal to create credibility and trust among your visitors.

Protect your login

Your login credentials are a gateway to your account and personal information (and when talking about websites, to your domain, site and emails, too). There are several things you can do to ensure that your login credentials are safe and secure, and that only you or the people you have authorized have access to your website:

Harden Your Passwords

Despite all the awareness created nowadays about weak passwords and the importance of never sharing login credentials with anyone, one of the most common credentials hacking is through guessing or brute-forcing easy-to-crack passwords. Having a long password, consisting of multiple characters and a combination of words, letters, numbers and symbols is an easy and super effective way to keep your accounts secure. Remember to use different passwords for different sites and apps, and never share your passwords with anyone, nor write them on publicly accessible places like post-it notes on your computer! Read more on the topic here.

Use 2-factor authentication

Regardless of how hard your password is, there’s still a possibility for a hacker to get to it through a brute-force attack, virus, malware or other. With 2-factor authentication enabled, a secondary step needs to be passed by anyone attempting to access your data. 2FA adds another layer of authentication, usually through a temporary dynamically generated code (accessible only from your phone or email, depending on the settings), which cannot be guessed or hacked and makes your login defense bulletproof!

  • For SiteGround Client Area, which is the gateway to your domains and sites, you can easily enable 2FA from Client Area > Login & Profile. 
  • For your WordPress application login, you can install and activate the SiteGround Security plugin and enable the 2FA feature. Download the plugin here, or install it directly through your WordPress admin area.

Monitor your website

Scan for malware regularly

There are numerous ways a website may get infected with malware – through compromised login credentials, infected or fake plugins and themes, corrupted software and more. Malware can have a serious impact on your site and online business. The best prevention for it is a secure web hosting platform and constant monitoring. If you’re a SiteGround customer, you can activate Site Scanner – a service that crawls your website on a daily basis and notifies you of potential malware and other threats. Just recently, Site Scanner helped save thousands of WordPress sites from particularly nasty malware.

Block suspicious traffic

There are cases where only the person managing a site can notice specific patterns or suspicious activity. We have provided easy-to-use powerful tools for blocking specific IP addresses or whole countries, enabling our customers to control who’s accessing their website and prevent unwanted visitors.

Back up your site regularly

While backups don’t protect you from hackers directly, they keep you safe from other unexpected events – a site update that may have gone wrong, an infected site that has to be reverted to a clean version, and any other situation where a copy of your website is all you need to bring it back online. We know how often backups can save an otherwise dire situation, so we do automated daily backups of all sites hosted with us and keep them for up to 30 days. You can easily restore your website, files, or databases for free in just a few clicks from Site Tools > Security > Backups.

Take special care of your WordPress

Being the most popular CMS in the world, WordPress is also one of the most popular targets for hackers. While all of the advice above applies to WordPress, there are a few additional things you can do to ensure that your WordPress site is well protected from bad actors and malicious software.

Keep your WordPress up-to-date

Keeping your WordPress up-to-date is essential for your website security. If your site is hosted with SiteGround, we’ve got this covered for you. All WordPress sites hosted with us get automatically updated to the latest stable WordPress version (only after we have thoroughly tested it). Free plugins are also auto-updated, depending on the user settings.

Add an extra safety layer with a trusted security plugin

There are WordPress-specific exploits and vulnerabilities that are best handled within WordPress itself. Some of our best WordPress engineers have developed the (free for all) SiteGround Security plugin that consists of a number of tools and features designed to keep your WordPress safe and secure. It helps site owners to disable XML-RPC if you don’t need it, add XSS protection, protect system folders from being injected with malicious files with just 1 click, and many more.

Avoid common usernames like “Admin”

Your login consists of two pieces – a username and a password. On many occasions, the username is something automatically generated by the platform where you register and you have no control over it, but on others, such as your WordPress application, you are in full control of what your usernames should be. Except, all WP installations come with the user “Admin” by default. And hackers know that, which means they are one step closer to accessing your site! That is why we suggest you disable all Admin users on your sites and create users with different usernames and equal to the Admin rights. You can disable the use of Admin and other common usernames with the free SiteGround Security plugin.

Limit login attempts

A standard behavior of unauthorized users is to try and guess your password (or username and password) on the login form by making multiple consecutive attempts for that. You can easily cut them off by limiting the number of consecutive unsuccessful login attempts they can make. After they reach the set amount, the IP from which they log in gets blocked for 1 hour. Use the free SiteGround Security plugin to activate this feature for WordPress sites.

Use a trusted web hosting provider with a security-first approach

As we mentioned in the beginning, protecting your website is a team effort and on our platform your website’s security is our number one priority. Here we want to recap some of the things we do and in case you are not a SiteGround client, you may want to consider these security essentials for any hosting provider you work with:

Server-level Web Application Firewall

The web application firewall monitors the traffic and blocks the opportunity for hackers to exploit many common application security holes. Although there are many solutions such as WordPress plugins, or third-party services to address that need, a server-level WAF is of utmost importance since it works with big data and real-time. That is why our dedicated Security Team constantly monitors various security bulletins for exploits and vulnerabilities, and immediately creates custom security rules, which they add to our smart and in-house managed Web Application Firewall. It protects all sites hosted with us out-of-the-box.

Brute-force prevention

Siteground has a sophisticated AI-driven bruteforce prevention system that for years has been stopping millions of bruteforce attempts per day (even hour)! And while this on its own is impressive, we recently made it even better. After the recent system upgrade, we have managed to reduce the amount of malicious traffic reaching your site by 95% and thus significantly minimizing the actual bruteforce attempts! No action is required on our clients’ end, they’re already using it. 🙂

DDOS protection

DDOS attacks are frequently used by hackers to bring down sites for different reasons – ransom demands, economical or business competition, political motives or simple vandalism. We have a system of software and hardware mechanisms that divert DDOS attacks, mitigate their impact, and eventually stop them. And the best thing is that you don’t have to do anything – we protect all sites hosted on our platform!

Managed PHP

Keeping PHP up-to-date is essential for keeping your website safe. Older PHP versions are often a gateway for vulnerabilities and malware, and a lot of web hosting providers tend to overlook this in order to make PHP management easier. We have developed a secure managed PHP solution that helps our customers keep their PHP updated to the latest stable PHP version.

On-demand traffic blocking (IP and Geo-Blocking)

There are cases where only the person managing a site can notice specific patterns or suspicious activity. We have provided easy-to-use powerful tools for blocking specific IP addresses or whole countries, enabling our customers to control who’s accessing their website and prevent unwanted visitors.

Smart Client Area & Site Tools Login

All SiteGround accounts are protected behind a smart login we have developed to recognize suspicious behavior and enforce additional client verification when an irregular pattern is detected. Our login system learns from your behavior – like the devices you’re usually using or the locations you often log from, for example – and knows whether a login attempt is coming from you or an impostor. In the latter case, a challenge is introduced – one that is easy to pass for the real account owner and very hard for anyone else.

Monthly Security Reports

There’s one more thing that often gets overlooked, but it’s important to include it in your website security strategy. You need to make sure that you keep an eye on your site’s security status regularly, yet this can take you much time, effort, and money. SiteGround clients receive free monthly security reports straight into their inboxes.

We perform automated security checks of our clients’ websites and then provide them with summary results in a user-friendly format, along with actionable tips on reducing the risk of malicious attacks, if we identify any weak areas.

These are the features that are essential for your website security. If you have all of them enabled, we’re confident that your website is well protected and you can have peace of mind that you have done everything in your power to secure your online business. We’d love to hear which of these features you’re already using and which are the ones you just found out about.

How to secure your WordPress website? (Video tutorial)

[subscribe_cta]